Law
The Safest Way to Be a Whistleblower

Blowing the whistle on wrongdoing is rarely a simple decision. Employees who witness illegal, unethical, or dangerous behavior often feel torn between wanting to do the right thing and fearing the consequences of speaking up.
Even though whistleblower protection laws exist, the reality is that many workers worry about retaliation, job security, and how their colleagues or supervisors will react. The safest way to be a whistleblower involves not only knowing your rights, but also understanding how to document concerns, choose the right reporting channel, and protect your privacy throughout the process.
The goal isn’t to make whistleblowing secretive or adversarial; it’s to make sure employees can come forward responsibly and safely, without putting their careers or well-being at unnecessary risk.
Understanding Your Legal Protections Before You Speak Up
Whistleblower protections vary depending on the type of misconduct involved and the industry in which you work. Federal laws cover retaliation related to workplace safety, corporate fraud, environmental violations, government contracting, financial reporting, and more. Plus, many states provide additional protections that apply broadly across different jobs.
Before reporting anything, it’s important to understand which laws may apply to your situation. Some laws protect whistleblowers who report internally, while others apply only when the report is made to a government agency.
Certain statutes cover employees even if they are mistaken about the misconduct, as long as they had a reasonable belief that wrongdoing occurred. Knowing these distinctions clarifies which steps are safest and most appropriate.
Documenting Concerns Carefully and Consistently
Documentation is one of the most important aspects of safe whistleblowing. If you observe misconduct, record what you saw as soon as possible while your memory is fresh. Include dates, times, locations, individuals involved, and anything else relevant.
Keeping your notes factual, neutral, and free of speculation preserves credibility and helps investigators evaluate the situation properly.
Documentation also matters if retaliation occurs. A sudden shift in workload, exclusion from meetings, write-ups for minor issues, or altered job expectations can all be subtle forms of retaliation. If you experience changes in how you’re treated after raising a concern, documenting those events can help demonstrate a pattern.
The safest approach is to store your notes securely and privately, in a place that cannot be accessed by coworkers or supervisors; transparency during an investigation is important, but you shouldn’t expose your documentation prematurely or carelessly.
Choosing the Right Reporting Channel
Whistleblowers typically have several reporting options, and choosing the right path depends on the nature of the misconduct.
Many organizations encourage employees to report concerns internally first, such as through a supervisor, HR department, compliance hotline, or ethics officer. Internal reporting can lead to quick resolution when leadership is trustworthy and committed to accountability.
However, not every situation is appropriate for internal reporting. If the misconduct involves senior executives, if the culture punishes people for raising concerns, or if the organization has ignored previous reports, external reporting may be safer.
Government agencies such as OSHA, the SEC, the EEOC, or state labor departments handle different types of complaints and often allow confidential or anonymous submissions.
Some whistleblower programs even offer financial rewards for reporting certain types of fraud or violations. These programs typically have strict confidentiality rules that protect whistleblowers throughout the process. Understanding the risks and benefits of each reporting pathway ensures you make the choice that aligns with both safety and effectiveness.
Maintaining Privacy While Following Proper Procedures
Privacy is one of the most important factors in staying safe as a whistleblower. While complete anonymity is not always possible, there are still steps you can take to protect your identity as long as reasonably possible.
Many organizations allow anonymous reporting through hotlines or third-party ethics systems. Government agencies also offer anonymous or confidential complaint mechanisms in many situations.
Even when anonymity can’t be guaranteed, you can still limit disclosure by avoiding unnecessary conversations and sharing information only with those responsible for handling the complaint. It’s also wise to avoid discussing your intentions with coworkers unless absolutely necessary.
Seeking Guidance When the Situation Is Complex
Whistleblowing can be risky, especially when the misconduct is serious or involves high-ranking individuals. In these situations, many people seek legal advice to help them weigh their options, understand their rights, and decide the safest reporting strategy.
Guidance can also help whistleblowers navigate conversations with investigators, maintain confidentiality, and organize their documentation effectively.
Seeking advice isn’t a sign of conflict; it’s a way to ensure you protect yourself throughout a stressful process. Whistleblower cases can be emotionally draining, and having support helps keep the focus on the facts and the law rather than fear or uncertainty.
Protecting Yourself
Being a whistleblower is brave, important, and often necessary, but it must be done safely. By understanding legal protections, documenting concerns, choosing the right reporting channels, maintaining privacy, watching for potential retaliation, and seeking support when needed, employees can protect themselves while helping ensure that wrongdoing is addressed.
On October 2, 2026, a federal judge in Nashville let a TCPA class action move forward over more than 150 ringless voicemails pitching debt relief, rejecting the usual argument that these messages aren’t “calls” at all. The case, Durham v. Clarity Debt Resolution, is one more sign that the workaround built to sidestep consumer phone law is coming apart on the vendors who sold it.
For years, companies that drop prerecorded messages straight into voicemail inboxes have told clients the trick is legal because nothing rings on the recipient’s phone. That theory has been losing in regulators’ offices and courtrooms since 2018. By 2026, it’s close to dead. Here’s what people still get wrong about ringless voicemail, one assumption at a time.
The “It Doesn’t Ring, So It Isn’t a Call” Argument Is Over
The whole business model rested on a semantic claim: if the recipient’s phone never lit up, no “call” was placed, and the TCPA didn’t apply. The FCC closed that door in late 2022. In a declaratory ruling, the agency found that ringless voicemail to wireless phones is a call made using an artificial or prerecorded voice, and therefore sits squarely inside section 227(b)(1)(A)(iii) of the statute.
The reasoning was blunt. These messages use the recipient’s wireless number to reach a mailbox tied to that number, and the phone still receives a notification. Calling that something other than a call elevated form over substance. If you’ve been told the technology occupies some gray zone, a plaintiff suing over one of these messages has a clear statutory path to pursue.
“We Got Consent Somewhere” Is Not a Compliance Program
Marketers often assume consent captured for one purpose covers everything that follows. That assumption is where most of the losses start. A ringless voicemail using a prerecorded voice to a cell phone requires prior express written consent for marketing, and prior express consent for most informational uses. The paperwork has to match the message.
A few patterns show up in the cases that go sideways:
- Stale lists. Phone numbers scraped or purchased from a third party, with no record of how or when the consumer agreed to anything.
- Scope creep. Consent collected for account notifications, then stretched to cover promotional pitches from a different line of business.
- Ignored revocations. A “stop” reply or verbal opt-out on a prior call that never made it into the suppression list the dialer actually reads.
- Reassigned numbers. The person who agreed years ago gave up the number, and the new subscriber is now getting messages they never asked for.
Any one of these can turn a routine campaign into a class action. All four show up in the same complaints over and over.
The 2026 FCC Rewrite Doesn’t Rescue the Practice
There is a lot of chatter in compliance circles about the FCC’s September 2026 draft order revisiting consent and opt-out rules. Some vendors are pitching it as a loosening that will give ringless voicemail breathing room. A careful read says otherwise.
The draft would narrow the delayed “revoke-all” requirement so a consumer’s opt-out could be read as applying only to the specific category of informational robocalls at issue. That is a change at the edges of how revocations get processed, not a reopening of the question of whether these messages count as calls. The core holding, that ringless voicemail is a prerecorded call to a wireless number, is untouched.
“The Statutory Damages Are Small” Isn’t True Either
The last myth is the one that gets businesses into real trouble. One message to one person sounds manageable, but a campaign is a different animal.
Multiply by a modest list, and the exposure runs into seven figures before anyone argues about class certification. The Nashville case cited at the top of this piece involves 150-plus messages to one named plaintiff alone. Vendors that pitched ringless voicemail as cheaper and lower-risk than a dialer campaign were pricing it against the ring, not against the lawsuit.
What to Do If You’re on Either Side of One of These Messages
If you’re a consumer who keeps finding prerecorded pitches in your voicemail, save them. The audio file, the timestamp, the number that “called,” and any transcript your carrier generates all matter. A pattern of messages from the same source, especially after you’ve told them to stop, is the record a case gets built on.
If you’re a business considering a ringless voicemail campaign, the honest answer is that the regulatory question is settled against the format. The path forward is the same one that applies to any prerecorded outreach: documented consent, a working revocation process, suppression that actually suppresses, and a hard look at whether the message needs to be prerecorded at all. The workaround is no longer a workaround.
Law
Your Smartwatch Just Became Evidence: What to Do When Heart-Rate, GPS, and Fitness Data Enter a Criminal Case
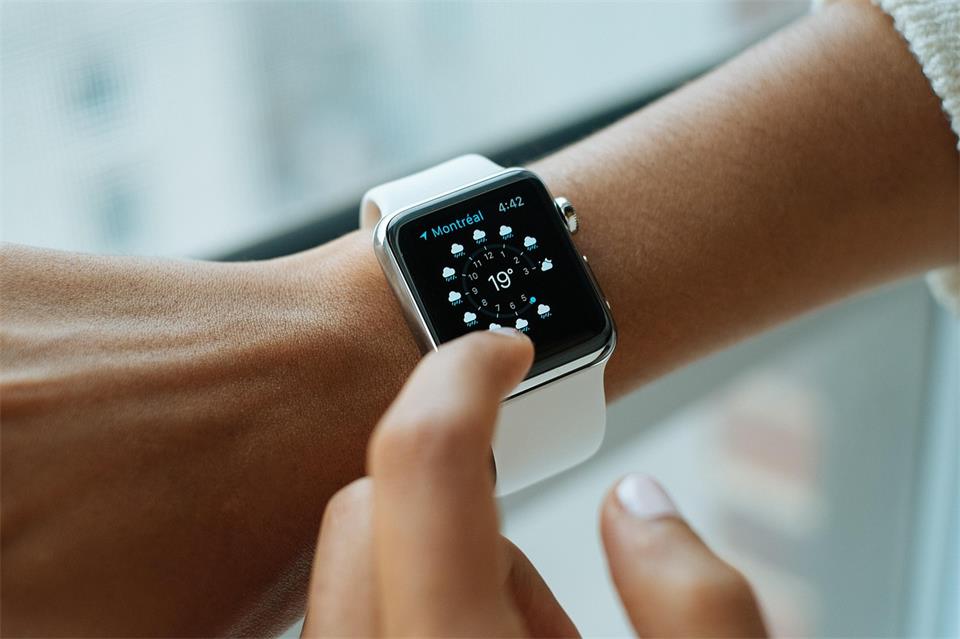
About one in five American adults wears a smartwatch or fitness tracker on a regular basis, and prosecutors have noticed. A device sold to count steps and nudge you off the couch now logs heart rate, GPS traces, altitude, sleep stages, and the second your pulse jumped. In a criminal case, those files become exhibits.
If you wear one, or someone close to you does, a handful of real decisions are waiting for you long before a detective ever calls. The worst time to work through any of them is under pressure, in the first hours after a serious incident.
Decide Whether to Keep Wearing It After an Incident
The reflex after any crisis, your own injury or someone else’s, is to pull the watch off and set it aside. Resist that reflex, and resist the opposite one too. A watch that keeps recording captures your real-time pulse, your location, the fact that you paced the kitchen for an hour. A watch suddenly removed, factory reset, or “lost” looks like exactly what it looks like.
Leave the device alone. Don’t delete the app, sign out of the cloud account, factory reset the watch, or hand it to someone else to hold.
“Once someone knows their wearable may contain evidence relevant to an investigation, trying to delete or alter that data can create a separate problem from whatever the data originally showed,” says SBBL Law. “The safer approach is to preserve the device and its data and let counsel determine what, if anything, needs to be produced.”
Decide Who Already Has Your Data
Most wearers assume their health metrics live on the watch. They live on a phone, in a vendor cloud, and often inside a secondary app that paid for the integration. Each of those custodians can receive a subpoena, a search warrant, or a preservation letter. Work through the full chain before you assume anything is private:
- The device itself. Local storage is small and recycled quickly, but recent sessions and the last sync token often sit there.
- The paired phone. The health app on your phone usually holds the richest, longest history, and it’s the easiest target in a consent search.
- The vendor’s cloud. Apple, Google, Fitbit, Garmin, and others store server-side copies that can be produced on legal process whether or not you still have the device.
- Third-party apps. Running, cycling, sleep, and fertility apps you connected years ago may still be pulling your data on a schedule you forgot about.
Consumer wearables mostly sit outside HIPAA, which surprises people. Fourth and Fifth Amendment problems come with that, including when the government can compel you to unlock a device versus when it has to go to the vendor directly.
Decide How Much to Trust the Numbers Themselves
Juries treat smartwatch readings like clock readings. They shouldn’t. Optical heart-rate sensors use photoplethysmography, which infers your pulse from light bouncing off capillaries, and the signal gets confused by motion, tattoos, dark skin, cold wrists, and loose bands. Stride and GPS have their own failure modes, especially indoors and under dense cover.
Prosecutors have won real cases with this data anyway. If you are the defendant, your decision is whether to attack the raw numbers, attack the interpretation, or both. The right answer depends on what the file actually shows when a forensic examiner pulls it, not on what the police report summarizes.
Decide Whether to Fight the Warrant or Fight the Reading
Two separate battles start once wearable data is in a case, and conflating them is a common mistake. One is whether the government should have gotten the data at all. The other is what the data actually proves.
The access fight runs through Carpenter v. United States, which required a warrant for historical cell-site location records held by a third party. Lower courts are still working out how far that reasoning stretches into continuous biometric data, and a motion to suppress is often worth filing even when the odds are mixed, because the record you build survives into appeal.
The reliability fight is different. A defense expert pulls the raw sensor file, shows the noise, points to the dropped signal, and explains why a sudden overnight spike might be the band shifting on the wrist rather than a sprint across a parking lot. Pick the fight that matches the evidence. Sometimes you file both motions, sometimes only one.
The device on your wrist is not neutral. It is a cooperative, always-on witness with no memory of what it saw and no instinct for self-preservation. The decisions above are the ones that let you, rather than the watch, shape the record.
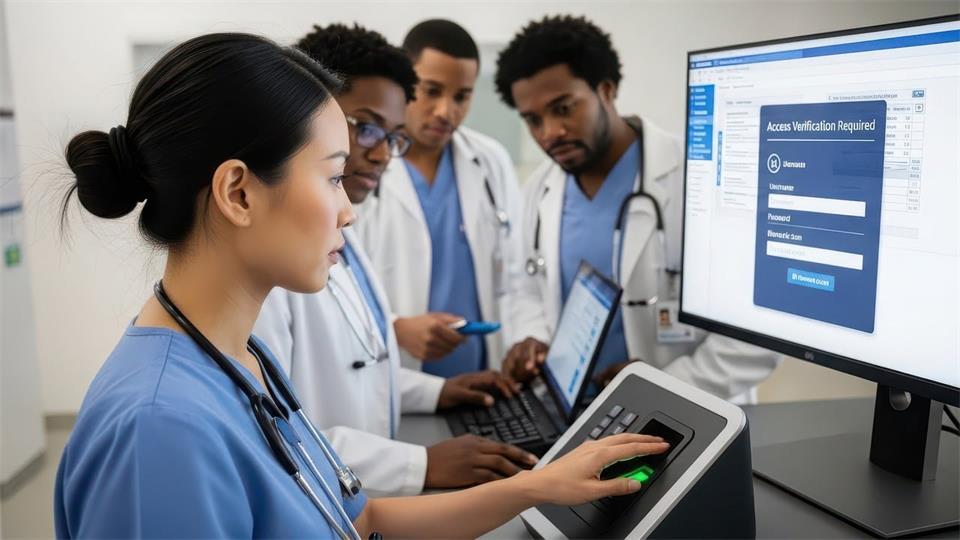
Can the anesthesia machine be subpoenaed in a malpractice case? Not the machine itself – but the streams of data it produces during a surgery, and the operating room recorder increasingly sitting alongside it, are showing up in litigation files that used to run on paper charts and memory.
The old fight over what happened on the table came down to the anesthesiologist’s handwritten record, the surgeon’s dictated note, and whatever the nursing team remembered weeks later. That’s no longer how it works in a growing number of hospitals. A modern OR generates a synchronized stream of vitals, ventilator settings, drug pushes, alarms, timestamps, and in some rooms audio and video of the procedure itself.
Each of those streams is a separate story with its own preservation clock. Below are the categories both sides are already fighting over, one by one.
The Continuous Vitals Trace on the Anesthesia Record
Modern anesthesia information management systems pull heart rate, blood pressure, SpO2, end-tidal CO2, and ventilator parameters straight from the monitors, at intervals measured in seconds rather than the five-minute handwritten dots that used to fill an anesthesia sheet. That fidelity cuts both ways.
A defense expert can point to a stable trace across a two-hour procedure and dismantle a claim that the patient was hypoxic for meaningful stretches. A plaintiff’s expert can zoom into the same trace and find the four minutes of desaturation nobody charted by hand.
Early survey work on anesthesia information systems found departments viewed the automated record as an asset for risk management rather than a liability, with no cases reported in which the automated record had hindered a defense. That remains the pattern most litigators see. When the vitals match the narrative, the record protects the clinician. When they don’t, the record is where the case starts.
The Drug Timestamps Nobody Used to Question
Every push of propofol, every reversal agent, every bolus of pressor now carries a machine-generated timestamp – from the pump, the dispensing cabinet, or the anesthesiologist’s entry into the AIMS. Plaintiff’s counsel can line those timestamps up against the vitals trace and ask why a pressor went in nine minutes after the pressure dropped. Or why the reversal agent shows an entry time that predates the end of the case by longer than the pharmacology would suggest.
The reverse also happens. Clean, contemporaneous drug logs have ended cases early, because the story a family was told at bedside, that no one responded for twenty minutes, gets contradicted by a dispensing cabinet withdrawal thirty seconds after the alarm.
Firms handling complex surgical injury cases now ask for these logs early, before anyone has to rely on memory.
The Audit Log Behind the Chart
The visible anesthesia record is only the top layer. Underneath sits the EHR audit trail: who opened the chart, who edited a field, when a late entry was added, and whether an addendum was backdated. Courts have leaned into this metadata. A recent narrative review of anesthesia EHR systems walks through how metadata discovery, including the Vargas v. Lee line of cases, has expanded what plaintiffs can request from a hospital’s electronic record.
For clinicians, the practical effect is simple. A chart entry made hours later that says the patient was stable during the procedure is not the same document as an entry made in the moment. The audit log knows the difference, and opposing counsel will too.
The OR Black Box Is Now in the Room
The newest layer is the operating room black box itself, a multi-channel recorder that stitches together room video, laparoscopic feed, audio, and device data into one synchronized timeline. Deployments have spread across hospitals in North America and Western Europe, tracking vital signs, equipment malfunctions, and surgical team performance alongside the procedure video.
These systems were built for quality improvement, not litigation. Faces are typically blurred, voices altered, and raw footage deleted on a short cycle, often around thirty days. That deletion window is the whole ballgame. If a patient or family suspects something went wrong, the preservation letter has to land before the recorder overwrites itself.
Miss the window and the strongest piece of objective evidence in the case is gone, without anyone doing anything wrong to make it disappear.
What Patients and Families Actually Have to Do
The through-line across every category above is time. Anesthesia traces are usually preserved with the medical record and stay retrievable for years. Device alarm logs, dispensing cabinet exports, and OR black box footage run on a different clock. Some overwrite in weeks.
If something felt wrong about a procedure, an unexpected ICU admission, a delayed wake-up, an injury the consent form never mentioned, the useful move is a written preservation request to the hospital’s legal or risk department that names the specific data streams, not a generic request for the file.
Ask for the AIMS export in native format, the pump and dispensing cabinet logs, the device alarm history, the EHR audit trail, and any OR recording tied to the case. A hospital that receives that letter in the first week has an obligation to hold the data. A hospital that receives it in the third month may have nothing left to hold.
The anesthesia machine has been taking notes the whole time. Whether anyone still has them when the case is filed is a separate question, and often the one that decides it.

Are Ringless Voicemails Legal? Understanding TCPA Rules and Violations

Why Creators Keep Misreading What a Sponsorship Actually Pays After Tax

Your Smartwatch Just Became Evidence: What to Do When Heart-Rate, GPS, and Fitness Data Enter a Criminal Case

How Operating Room Data Recorders Are Now Tackling Medical Malpractice Fights

The Message You Sent at 11 p.m. May Show Up in Court: Co-Parenting Apps vs. Everyday Texts as Evidence

The Number vs. The Story: How Coefficient of Friction Is Reshaping Slip-and-Fall Cases

How ICX Global Works From Sign-Up to Market Access
-
 Captions5 years ago
341 Sexy Captions to Fire Up Your Instagram Pictures
-
Captions5 years ago
311 Night Out Captions for Instagram and Your Crazy Night
-
Captions5 years ago
245 Saree Captions for Instagram to Boost Your Selfies in Saree
-
Captions5 years ago
256 Best Ethnic Wear Captions for Instagram on Traditional Dress
-
Captions5 years ago
275 Deep Captions for Instagram to Express Your Thoughts
-
Captions5 years ago
230 Blurred Picture Captions for Instagram
-
Quotes5 years ago
222 Nail Captions for Instagram to Showcase Your Fresh Manicure
-
Captions5 years ago
211 Laughing Captions for Instagram | Laughter Is the Best Medicine